Our take: Best for startups and security teams needing affordable, audit-ready penetration tests and continuous source code security scanning without expensive human testers.
Main limitation: Pentests and source code audits require the paid Pro plan; Pro usage limited to 40 credits per month
By the AI Tool Atlas editors.
Based on the vendor's official documentation; we have not tested this product hands-on. What “documented overview” means
Who AISafe Labs fits
Best for startups and security teams needing affordable, audit-ready penetration tests and continuous source code security scanning without expensive human testers. Based on the vendor's documentation, not on a hands-on test.
Best for: Startups needing compliance-ready pentest reports
Also a good fit for
Security teams with budget constraints
Open-source maintainers
Continuous security monitoring in CI/CD pipelines
Consider another tool if need unlimited pentest capacity (Pro limited to 40 credits/month)
Or if
Require on-premises deployment at scale (Enterprise custom pricing)
Need advanced AI model customization (requires own LLM API key on Enterprise)
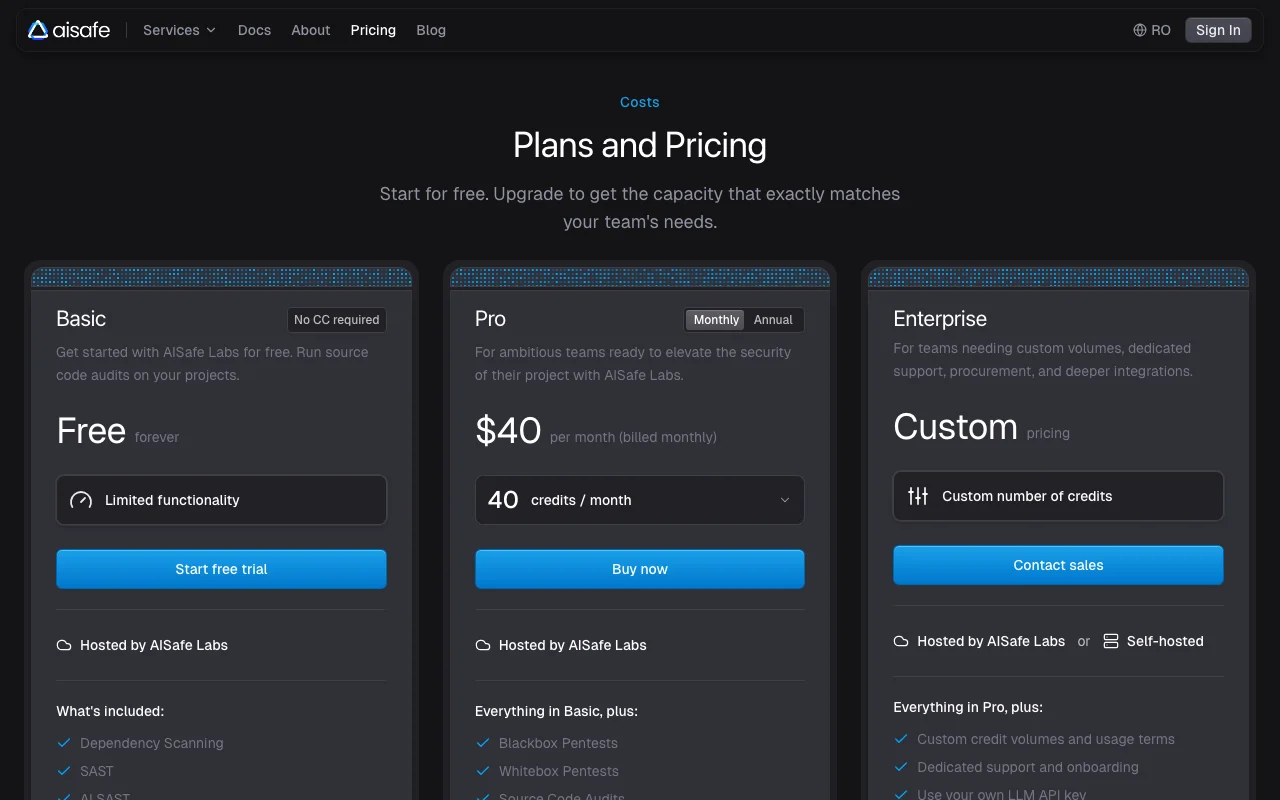
AISafe Labs pricing and usage limits
Prices checked Sep 29, 2026 on the official US pricing page. Official pricing ↗ Prices and limits change often.
Vendor pricing page re-checked automatically 11 days ago: no changes detected.
The official AISafe Labs pricing page as we saw it. aisafe.io, captured Oct 1, 2026
Free access and trial conditions
Basic plan is free forever with no credit card required. Limited functionality includes automated scanning (dependency, SAST, secrets, license, IaC) and single-project source audit testing.
No explicit trial; free plan serves as trial. Pro plan can be cancelled any time if on monthly commitment, or at end of annual term if on annual commitment.
For: Enterprises with high testing volume, regulated industries, custom workflows, and on-premises requirements
Includes
Everything in Pro, plus:
Custom credit volumes and usage terms
8 more
Dedicated support and onboarding
Use your own LLM API key for custom models
Priority Support in Slack
Team roles and permissions
Custom integrations and reporting workflows
Procurement, invoicing, and security review support
Self-hosted deployment option
On-premises or air-gapped deployment
API included
Usage caps, credits and extra costs
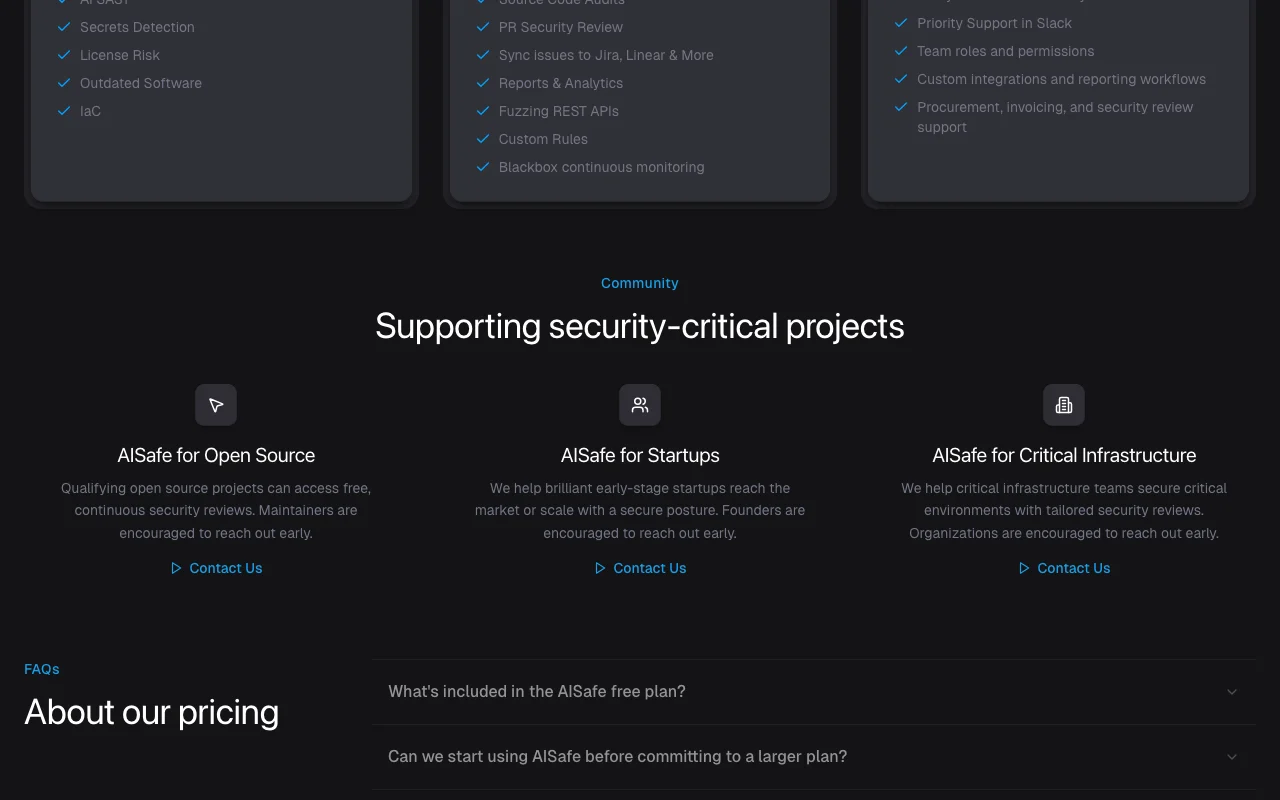
No pro-rata refunds on cancellation. AISafe for Open Source, Startups, and Critical Infrastructure may offer free or reduced access (contact required).
Not mentioned
What is AISafe Labs, and how does it work?
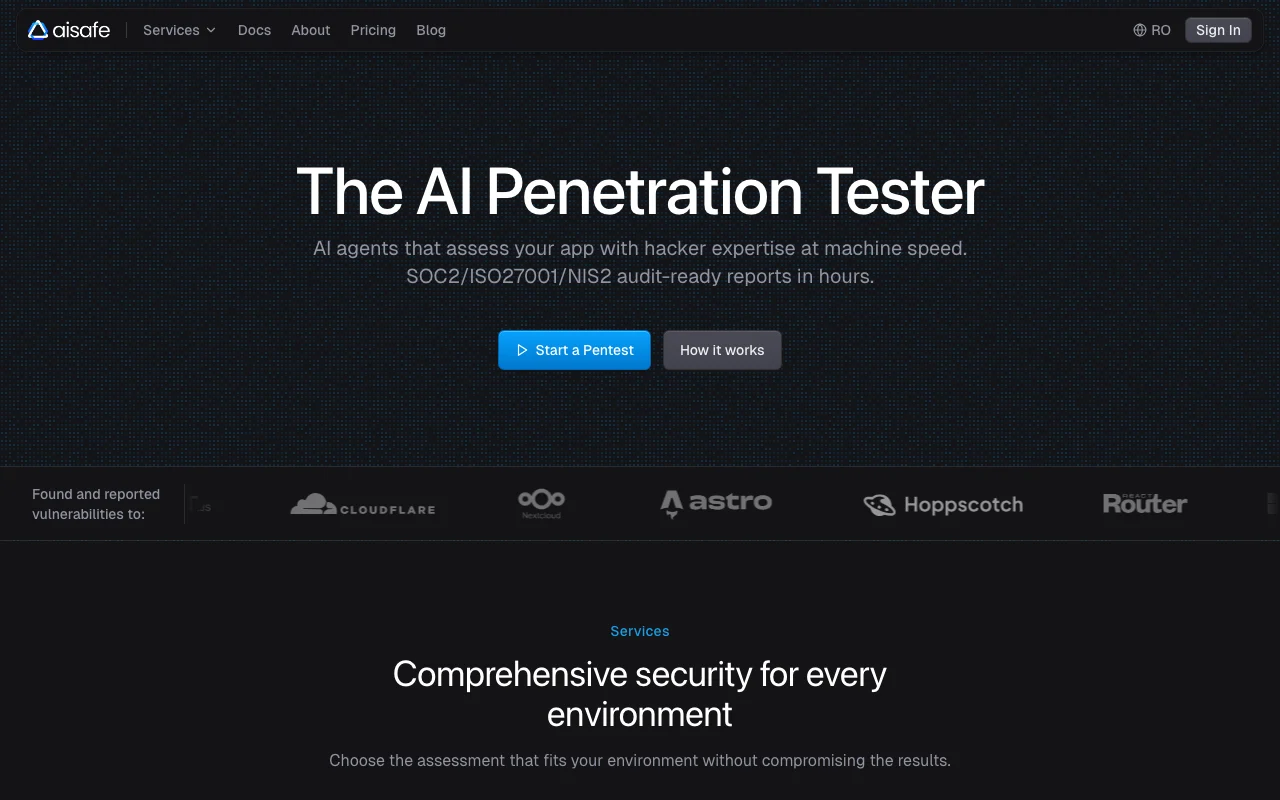
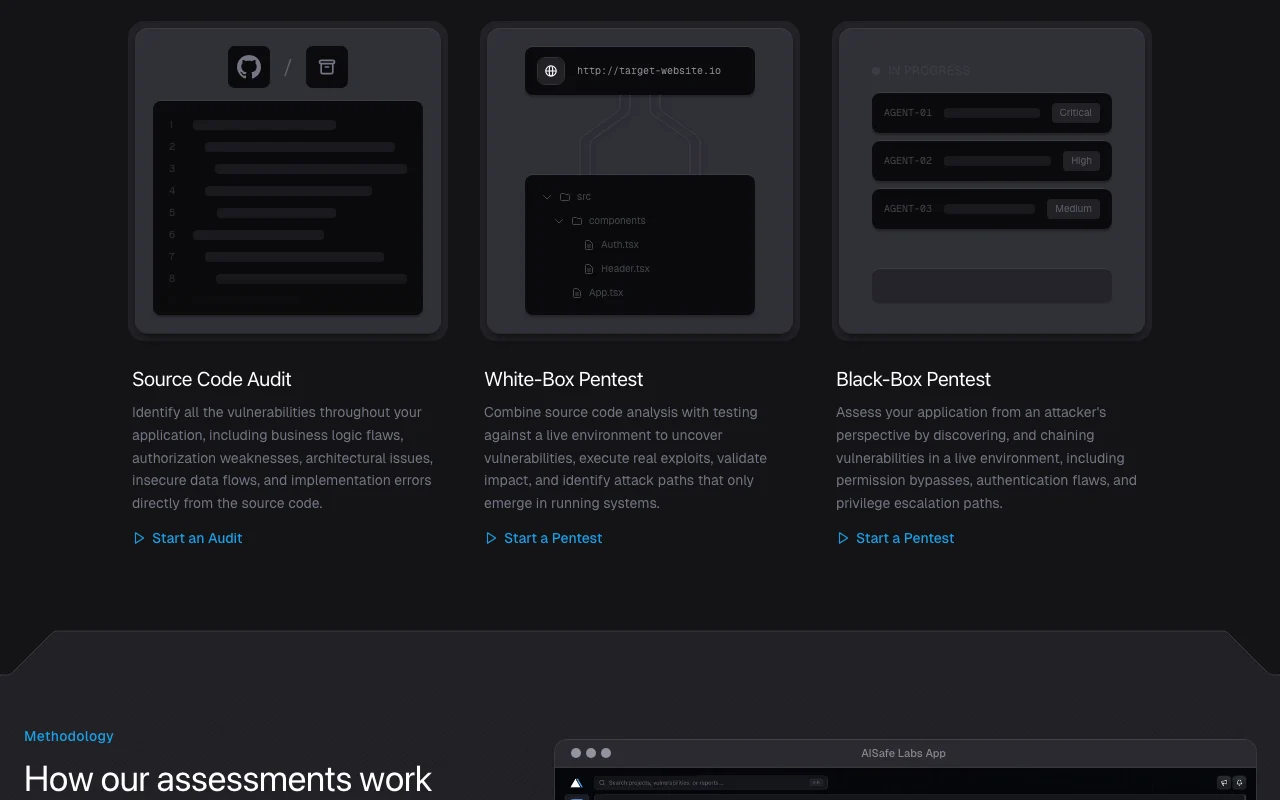
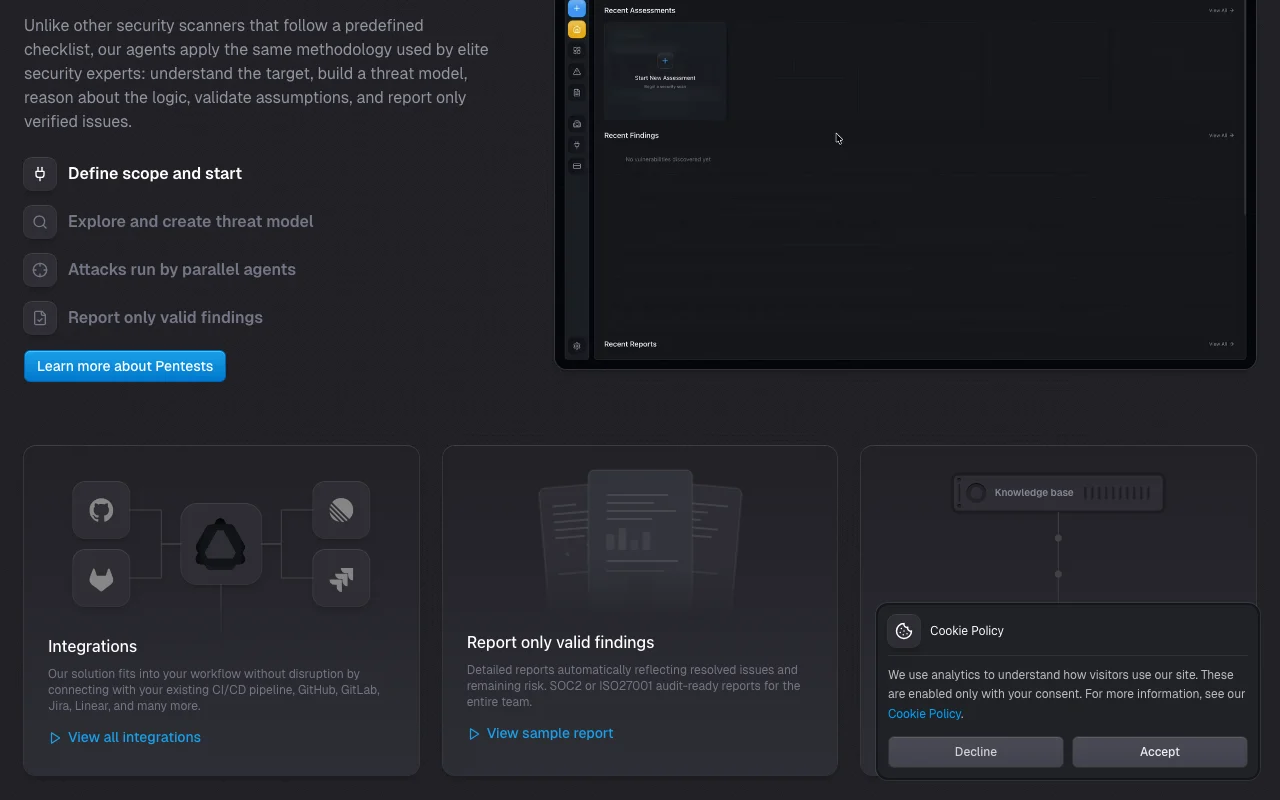
AISafe Labs offers AI-driven security assessments: source code audits, white-box pentests (combining source code analysis with live environment testing) and black-box pentests (external attacker perspective). Reports are aimed at SOC2, ISO27001 and NIS2 audits. A free Basic plan covers dependency scanning, SAST, AI SAST, secrets detection, license risk and IaC scanning. The Pro plan adds pentests and PR security review. Enterprise adds self-hosting and custom volumes. The platform applies elite security methodology: understand target, build threat model, reason about logic, validate assumptions, report only verified issues.
AISafe Labs's official site: how the product presents itself. aisafe.io, captured Oct 1, 2026
What you provide and what you get back
What you give AISafe Labs and what comes back, from its documentation
You provide
Source code (GitHub, GitLab integration)
Live application URLs (for black-box and white-box pentests)
Application artifacts and dependencies
You get back
SOC2/ISO27001/NIS2 audit-ready security reports
Vulnerability findings with severity levels and remediation guidance
PR security review results
Continuous monitoring and endpoint tracking
Where you can use it
Platforms
Web (SaaS), Self-hosted (Enterprise)
Account
Required
Models / versions
AI agents with parallel execution; supports custom LLM API keys on Enterprise
Feature overview on the official site. aisafe.io, captured Oct 1, 2026
Black-box and white-box AI pentests
Automated penetration testing from attacker perspective (black-box: no code access) or combined with source analysis (white-box); discovers and chains vulnerabilities in live apps Identifies real exploitable vulnerabilities without false positives; chains attacks to show impact
Access: Pro ($40/month) and Enterprise; white-box combines source code analysis with live environment testingLimit: 40 credits/month on Pro; complex apps consume more creditssource (opens in a new tab)
Source code audits
Identifies all vulnerabilities in source code including business logic flaws, authorization weaknesses, architectural issues, insecure data flows, implementation errors Finds vulnerabilities before production; supports threat modeling and risk assessment
Access: Free tier can test single project; Pro and Enterprise for unlimited auditsLimit: Free limited to one project; requires source code accesssource (opens in a new tab)
SAST, AI SAST, dependency and secrets scanning
Dependency tracking, license risk analysis, outdated software detection, secrets detection, IaC scanning; includes both traditional and AI-powered SAST Continuous scanning for known vulnerabilities and misconfigurations; prevents supply chain attacks
Access: Free on Basic plan and aboveLimit: Continuous scanning vs on-demand pentests at different access tierssource (opens in a new tab)
PR security review and continuous monitoring
Automated security review of pull requests against threat model established during assessment; continuous monitoring of endpoints and permissions Prevents regressions and security degradation as code evolves; ensures security invariants remain intact
Access: Pro and Enterprise; integration with GitHub, GitLabLimit: Requires prior assessment to establish threat modelsource (opens in a new tab)
AISafe Labs pros and cons
Where AISafe Labs is strong
Free plan without credit card Low barrier to entry for teams to validate AISafe fit before payingdocumentedsource (opens in a new tab)
Pro plan price published in USD ($40/month) Transparent pricing; easy to budget and comparedocumentedsource (opens in a new tab)
Self-hosted option on Enterprise On-premises deployment for regulated industries and air-gapped environmentsdocumentedsource (opens in a new tab)
Free programs for qualifying open-source projects, startups, and critical infrastructure Reduces cost for non-commercial and early-stage deploymentsdocumentedsource (opens in a new tab)
Limitations to check before paying
Pentests and source code audits require the paid Pro plan Free tier limited to automated scanning; core security testing requires Pro subscriptiondocumentedsource (opens in a new tab)
Pro usage limited to 40 credits per month Large or complex apps may exceed credit allocation; high-velocity testing requires Enterprisedocumentedsource (opens in a new tab)
Self-hosting only available on Enterprise with custom pricing On-premises deployment requires enterprise agreement; no published pricingdocumentedsource (opens in a new tab)
No dedicated support on Pro plan Pro users limited to community Discord; dedicated support requires Enterprisedocumentedsource (opens in a new tab)
How to use AISafe Labs for running a security assessment (audit or pentest) on a web application
Set up AISafe Labs
Go to aisafe.io and sign up for free (no credit card required)
Create an account and log in to the dashboard
Define scope: provide source code repository URL or application URL
Choose assessment type: source code audit (free tier single project), black-box pentest, or white-box pentest (Pro)
Start the assessment and wait for report generation (hours for pentests)
Example: running a security assessment (audit or pentest) on a web application
On Pro plan: navigate to 'Start a Pentest' and enter target URL
AISafe agents explore the app, build threat model, and run parallel attacks
Agents validate each finding to minimize false positives
Report is generated with findings, severity, remediation steps, and compliance mapping
Optional: enable PR security review to monitor future changes against the threat model
Review and export the result
Dashboard shows assessment status (in progress, completed)
Report is downloadable in audit-ready format (SOC2/ISO27001/NIS2)
Vulnerability findings display severity, description, and attack path
Verification: reported vulnerabilities are confirmed exploitable, not false positives
AISafe Labs integrations and API
Plan comparison on the official pricing page. aisafe.io, captured Oct 1, 2026
AISafe Labs has no public API in its official documentation. Enterprise supports custom LLM API keys (e.g., OpenAI, local models) for custom AI agents
Privacy, data use and commercial rights
Summarized from the vendor's current policies; this is not legal advice and a vendor's badge is not an independent audit.
How your inputs and outputs are handled
Source code and application data are processed for security assessment. Findings and reports are stored encrypted. Personal data (contact, professional) collected only via forms and newsletter signup.
Not mentioned; privacy policy does not indicate training data collection
Not explicitly stated; data stored encrypted on cloud infrastructure or self-hosted on Enterprise
Commercial use and plan restrictions
Permitted; designed for commercial security assessments
No privacy differences between tiers; all data processed under same privacy policy
Controls for business users
GDPR compliant (based in EU/Romania)
Data stored encrypted
No special category data collection
Processors: Cloudflare, Google Cloud EU, PostHog EU, Peek EU
Standard Contractual Clauses for international transfers
Basic plan includes Dependency Scanning, SAST, AI SAST, Secrets Detection, License Risk, Outdated Software, and IaC scanning. You can also test source code audits on a single project. No credit card required. source (opens in a new tab)
Can we start using AISafe before committing to a larger plan?
Yes. Teams can start with the free plan, validate how AISafe fits their workflow, and upgrade only when they need more assessment capacity or deeper support. source (opens in a new tab)
Does the Pro plan include support?
The Pro plan is self-serve with no dedicated support. Community help is available in the Discord server. Dedicated support is available only in the Enterprise plan. source (opens in a new tab)
Is AISafe secure? Where is my data stored?
Yes. All data, including source code, findings, and secrets, is stored encrypted. For hosted plans, data is stored on secure cloud infrastructure. For self-hosted plans (Enterprise), data stays wherever you decide to deploy AISafe. source (opens in a new tab)
Can I cancel my Pro plan subscription?
Yes. If on a monthly commitment, you can cancel anytime and the subscription ends at the close of your current billing cycle. If on annual commitment, cancellation takes effect at the end of the annual term. AISafe does not offer pro-rata refunds. source (opens in a new tab)
Not verified: Annual pricing for Pro plan (annual option mentioned but not detailed); Specific credit cost per assessment type; Enterprise pricing model and typical costs; SLA and response time for report generation; Maximum project size/complexity that can be tested.
How we documented and maintain this page
Every fact about AISafe Labs above comes from the 3 official pages listed here, last compared on Sep 29, 2026; we have not run AISafe Labs ourselves, so it has no editorial score. How we check and re-check pages.
Article updated Oct 10, 2026; prices checked Sep 29, 2026. Outbound links to vendors are plain links; we do not earn commissions. How we review · Report an error